Pagina's

donderdag 7 februari 2019

How to protect your data from theft

Data, whether owned by a company or a private individual, is becoming quite a challenge to protect because of the many possibilities and methods of cyber attacks. According to research, insider cyber attacks have become more significant than outsider attacks. Secure Channels CEO Richard Blech discusses ways to secure your online data from being stolen.


Form a security culture. If you are protecting important data in your home or office computer, a practice promoting security should be ingrained. Prevent random users from downloading, or any unauthorized person from plugging in USBs or hard drives into your device.

Image source: mashable.com
Invest in a good anti-virus software. Richard Blech stresses the invaluable contribution of a decent anti-virus software that can scan https traffic to protect you from phishing attacks. By scanning your encrypted web communication, you are able to analyze the content of websites you frequent. Competent anti-virus software can also match signatures of questionable behavioral patterns of malicious websites.


Encrypt your hard drive. Do this as an added security measure so cyber thieves cannot access your data even if your computer or device is stolen. Modern operating systems and hardware support offer default encryption mechanisms that won’t slow down your computer. You can even do this with your mobile device in case you frequently use it to exchange valuable data.


Richard Blech completed his degree in Business Administration from the Business School Lausanne. He is the CEO of Secure Channels and an investor, innovator, and entrepreneur. Richard is also managing member of Imperium Management LLC, actively investing in technologically advanced projects. He is a resolute advocate of disruptive technology, holding vested interests in cyber defense and digital content. For more articles like this, visit this page.

donderdag 17 januari 2019

Healthcare industry: A prime target of cyberattacks

In the U.S., healthcare is the second largest sector of the economy. It accounted for around 18 percent of the nation’s total GDP in 2017. Unfortunately, the sector size also makes it vulnerable to cyberattacks. As a matter of fact, the healthcare industry is twice as vulnerable to cyberattacks than any other sector.

Image source: cybersecurity-review.com
There are plenty of reasons hackers target healthcare, such as the following:


Highly valuable data: Healthcare organizations hold a great amount of patient data, which can include highly sensitive and private information, such as full names, social security numbers, addresses, contact details, birth information, and more. Hackers can sell such information on the black market or monetize it through blackmail. For example, in early 2018, a U.S. hospital had to pay $55,000 to cybercriminals after a ransomware attack.

Image source: noobpreneur.com
Ease of attacks: Nowadays, consumers prefer and sometimes even demand quick service and instant access to medical information, scheduling, and other services. Healthcare organizations have then invested in remote services, Internet-based consulting, cloud technologies, IT integration, Internet of Medical Things, and other similar technologies. These, unfortunately, can also provide additional opportunities for cybercriminals to attack, especially if insufficient resources are spent on cybersecurity. Compliance challenges are also commonplace in the healthcare industry, which may make it more difficult for organizations to include additional budget on cybersecurity.


Richard Blech is a resolute advocate of disruptive technology, holding vested interests in cyber-defense and digital content. Read more about these topics by checking out this blog.

How blockchain technology helps protect your data

Blockchain technology relies on the formation of constantly growing record lists called blockchains which are secured via cryptography. It’s the principal transaction innovation behind the rise of digital money or cryptocurrency. But how exactly does it aid in better protecting your data?

Image source: greentechmedia.com

For one, actual physical transfers for any blockchain-based transaction happen independently of the sending of tokens that contain any asset’s metadata. These virtual ledgers carry everything from maps, images, documents and, well, money. And blockchain aids immensely in eliminating wrong or illegal transactions because by nature it is dependent on a consensus between the mentioned physical and virtual transfer.


Moreover, blockchain makes your data hard to hack, as it stores, for example, your financial information across a vast network of computers or servers. If one gets compromised, it doesn’t mean that the others will be because they rely on different nodes. In the first place, hacking even just one blockchain server and altering one’s records is extremely difficult if not altogether impossible.

Image source: aithority.com

Even the World Economic Forum agrees that the distributed-ledger system provided by blockchain will be crucial in storing and protecting data, saying that 10 percent of worldwide gross domestic products will be on these ledgers as early as 2027. Financial institutions everywhere must adapt and migrate their bonds, stocks, property deeds, etc. onto these most-welcome and smart grids if they are to better maintain customer trust and loyalty down the line.


Secure Channels CEO Richard Blech is a managing member of Imperium Management LLC. He actively invests in technologically advanced projects and holds a vested interest in cyber defense and digital content as he is a determined advocate of disruptive technology. For related posts, visit this blog.

maandag 12 november 2018

Common cybersecurity mistakes made in enterprises

Image source: wipro.com

Now that cybercriminals are targeting more and more enterprises, enterprises should be more aware of ongoing cybercriminal campaigns and fortify their defenses. More than ever, cyberattacks have been getting a lot of attention from the media because of attacks like WannaCry. However, there are still companies that are reluctant to change their security practices. Here are some of the common cybersecurity mistakes made by companies which cybercriminals capitalize on.

Weak passwords Weak passwords can easily be guessed or bypassed by special software. People generally use weak passwords because of ease of use. But the same ease of use goes both ways as vulnerable passwords make hacking that much easier. A strong password includes upper and lower case letters, numbers, and special symbols.

Bad email practices Cybercriminals often go after weak and possibly non-tech savvy employees when targeting large companies. And with email being the most common attack vector for most cyberattacks, having bad email practices can lead to a security breach. Bad email practices include downloading files and clicking on links from unknown senders.

Image source: engineering.nyu.edu
Outdated security tools A lot of companies rely on limited resources when it comes to cybersecurity. Instead of devoting resources for improved cybersecurity, they rely on built-in security systems which may not be the best option to fend off today’s threats.

Patching delays Microsoft as well as other operating systems release patches regularly to fix bugs in their software. However, some companies choose not to update their systems because of the downtime needed to update all their computers. This makes computers susceptible to attacks which abuse certain vulnerabilities.

Richard Blech is an entrepreneur, investor, and innovator. He is the Chief Executive Officer of Secure Channels, a security solutions company that provides innovative state-of-the-art designs that complement clients’ existing investment in security. For more reads about him and the company, visit this website.

donderdag 18 oktober 2018

Why entrepreneurs should prioritize innovation

Image source: innovationexcellence.com
Innovation is a continuous process and it’s the secret to entrepreneurship. For successful entrepreneurs, leading innovations in their chosen field is a day-to-day job. They are lifelong learners and have dedicated their lives to finding the newest solutions to fundamental problems.

Growth

Without innovation, there will be no growth. Entrepreneurs follow timelines for growth and success. Prior to expansion, new ideas must be developed and presented to the world for consumption. The market is always on the lookout for the next best thing. Only through innovation can a company become the fastest-growing in its field.

Image source: uni-bayreuth.de

Visibility


A company can only stand out among its competitors through innovation. Competition is a constant. Conceptualizing the newest and brightest ideas and projects can turn the heads of consumers and, by providing proper customer experience, a company can gain loyal brand followers.

Delivery

A company that delivers and exceeds customers’ expectations will have a place in the industry. Consumer needs are changing by the minute, and meeting them feeds into the expansion goals. Through research, businesses can predict the needs of their customers and set the direction for innovation development. When needs are met, customers are pleased. Customers will keep coming back when they know a company knows their needs and constantly meets them with excellence. Innovation is as important as customer experience.

CEO of Secure Channels Richard Blech is an entrepreneur, investor, and innovator. He focuses on data security, technology, and strategic alliances. Learn more about data security and innovations by subscribing to this blog.

Tips for enhancing data security

Image source: insights.dice.com
` Whether in the context of huge companies or of a private individual, a data breach is an outright alarming concern. No one is safe from cybercrime in this age of the internet, with most of our private information, communication, and transactions being brought online.

You should be extra mindful of the importance of gaining optimal data security. Ensuring your privacy begins with an awareness that everyone is a potential target for hackers. And if businesses are to run smoothly and focus on improving brand reputation and customer service, they must first establish clear data security infrastructure and policies.

This begins with knowing your most valuable data and prioritizing them in any protection protocol. For individuals, these data will be comprised of bank and security account numbers, PINs, and passwords. For businesses, key data are the ones that would cripple the company if compromised. It’s highly advisable that owners and managers limit employee access to such sensitive information.

Image source: paychex.com
Make it a habit to back up your data regularly. Set a fixed date for copying files to portable physical devices and online storage systems, whether on a daily, weekly, or monthly basis. Take the initiative, as you’ll never know when that drive is going to crash, or when a breach will occur. Moreover, automate backups if possible using solid software programs.

Lastly, if your passwords are tied up to birthdates and names of family members, then they are weak and easily discoverable. Put effort in making passwords stronger by making them longer and comprised of alphanumeric combinations. It goes without saying that these should be unique to each employee and not canopy access codes.

Secure Channels CEO Richard Blech holds a vested interest in cyber defense and digital content. An entrepreneur, investor, and innovator, he determines market trends that are not only lucrative, but also pave the way for technological advancements across the globe. More info on Richard and his work here.

woensdag 8 augustus 2018

Cyber Threat Intelligence: An Overview

It’s a concept often mentioned and discussed in light of recent cyber crimes on online data and information. But what is cyber threat intelligence really all about, and how does it deter these cyber attacks and protect private data online? 

Image source: Pixabay.com

Cyber threat intelligence is the collection of information from open source intelligence, social media, human intelligence, technical expertise and resources, or intelligence from the deep and dark web. It seeks to research and analyze trends and technical developments in the areas of cybercrime, hactivism, and cyber espionage or cyber spying. The goal is to create preventive measures based on those accumulated data and maintain international security. 

Intelligence tactics, techniques, and procedures have existed long before cyberspace. They are ultimately rooted in defense, and in a military context the principles seek to know the intent of the opponent to inform battle strategies, or to prepare for an attack. 

Cyber threat intelligence is hardly an end-to-end process. It also goes by the intelligence cycle, where data collection is undertaken, results are analyzed, and the resulting intelligence is disseminated and evaluated in light of new information and consumer feedback. As technical intelligence, for example, one may look at indicators of specific malware. Meanwhile, operational intelligence is concerned with the details of an incoming attack and assesses the organization’s ability to determine future threats. 

Cyber threat intelligence has proven beneficial to every level of state, local, tribal, and territorial government entities, from senior executives to police chiefs to policy makers. It also offers value to experts such as security officers, terrorism analysts, and accountants. 

Image source: Pixabay.com

Richard Blech is an entrepreneur, investor, and innovator. He is also the CEO of Secure Channels, a company that comes up with solutions designed to be customizable to its clients’ environment without compromising the level of protection it provides while avoiding additional maintenance and support efforts by support teams. Learn more on this page.

donderdag 19 juli 2018

What Is Disruptive Innovation, Exactly?

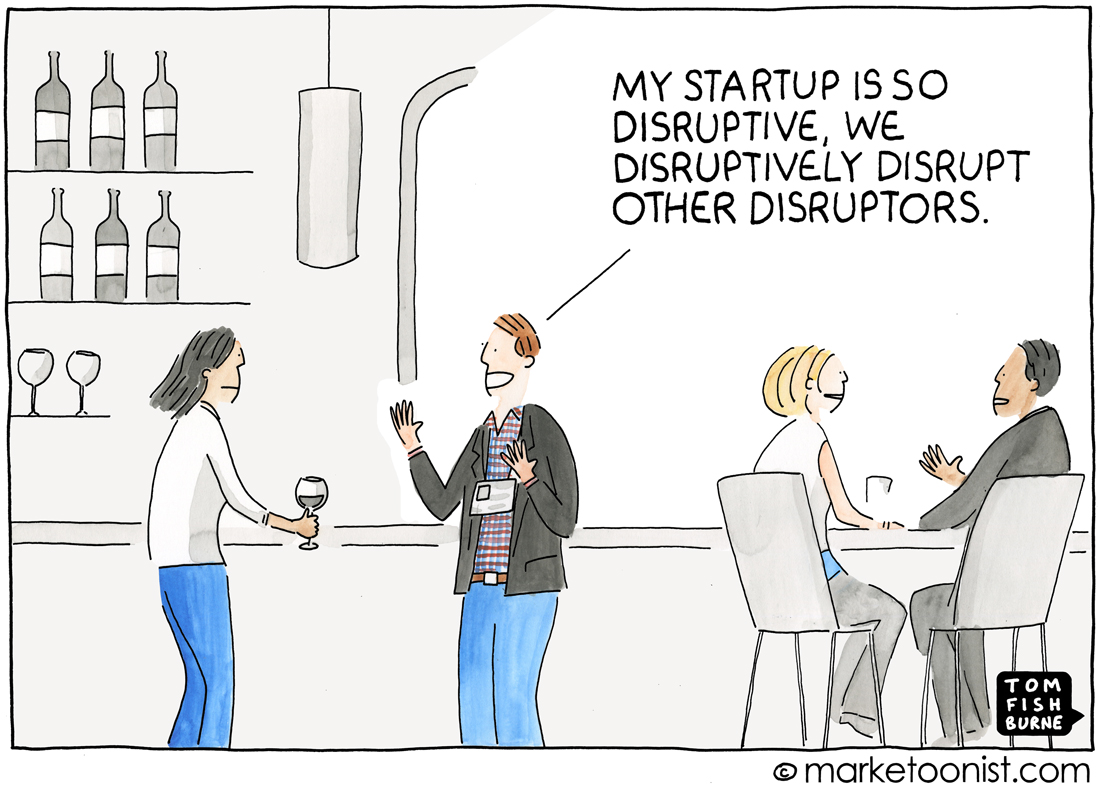
Disruptive innovation is a business term which refers to any landmark technology that “disrupts” or alters both existing market and value networks by creating a new one and displacing established leaders in the industry.

The term certainly doesn’t have any negative connotation as it is crucial in generating business ideas, discouraging complacency, putting inventors and startups in the limelight, and generating healthy competition. A good example of an early disruptive innovation is the mass production of the Ford Model T in 1908, which changed the way businesses look at transportation. This led to widespread access to cheap cars for everyone.

Image source: marketoonist.com

Most disruptive innovations are not necessarily the brainchildren of industry leaders but entrepreneurs looking to find niche markets. Entrepreneurs often have to study the profitability of the venture; for this reason, most disruptive innovations don’t attract financial support early.

However, with the huge success of now world-renowned groups like Netflix, Uber, Skype, and Google Apps, more startup ventures are being funded as the next revolutionary business venture.

Image source: thevideoink.com

All in all, the continuous arrival of disruptive innovations will just benefit the typical consumer, as the latter’s needs are prioritized. Disruptive innovations tap segments of the market that have been neglected by established companies. Whether new products and services rise to the level of disruption or not depends on the offering, time, and gained market support. And we can’t complain as, in the end, disruptive innovators only make our lives better.

Secure Channels CEO Richard Blech is a managing member of Imperium Management LLC, actively investing in technologically advanced ventures. A resolute advocate of disruptive technology, Richard has strong interest in cyber defense and digital content. For more on his professional background, visit this website.


woensdag 30 mei 2018

Safety Measures: Learning From The Atlanta Ransomware Attack

The Atlanta ransomware attack that occurred in March 2018 has prompted discussions between IT professional and cybersecurity experts based in the U.S. and U.K. The agenda was how to detect and prevent future attacks.

Image source: tripwire.com

Upon further investigation, it was deemed that the IT group in Atlanta took weeks before updating their systems with patches provided by Microsoft. This just shows how important it is to follow basic safety measures. 

Here are some more reminders for the public to minimize the damage caused by ransomware.
  • Backup all critical data regularly. Many ransomware hackers have no use for the data they encrypt, which means data backups render ransomware useless for hackers.
  • As soon as they become available, install security patches for operating systems and any other devices, and install updates whenever you are notified. Patches and updates fortify any vulnerabilities in the system.
  • Anti-virus and anti-malware programs should be installed on all devices and operating systems.
  • Administrators should have contingencies in case hackers successfully deliver the ransomware. These contingency plans should allow the continued operation of government services while IT experts find a way to deal with the attack.
  • Hacking tests should be conducted on government systems on a regular basis. This identifies holes in the system, which should either be patched up or removed entirely from data servers. 

Image source: bankinfosecurity.com

Richard Blech is the CEO of Secure Channels, a company conceiving solutions designed to be customizable to its clients’ environment without compromising the level of protection it provides and reducing maintenance costs. For more tips on cybersecurity, visit this blog.

dinsdag 17 april 2018

A Quick Look At Cyber Threat Intelligence

For today’s businesses and organizations, it is no longer enough to deal with cyberattacks once confronted by them, or act once damage has already been done. As a preemptive move, companies allocate time and resources to protective strategies such as cyber threat intelligence (CTI), is which organizing, analyzing, and refining information about potential or ongoing cyberattacks that threaten them.
Image source: Pixabay.com

CTI is mainly intended to help companies and organizations know and understand the risks of common and severe threats from the outside, ranging from zero-day threats to advanced persistent threats or APTs. It involves detailed information about certain threats to help protect them from the most extensively damaging attacks that could occur in the future.

CTI can provide different benefits to different people in the organization. For directors and executives, it can help improve situational awareness and offer scalable, repeatable processes and platforms to leverage their security strategy. It will also help Chief Information Security Officers (CISOs) to educate senior leadership on current and emerging risks, as well as the most effective ways to manage them.

This isn’t an end-to-end process, but instead a circular process known as the intelligence cycle. In the cycle, requirements are stated, data collection is implemented and evaluated, and the results are analyzed to produce intelligence reports. The resulting intelligence is disseminated and revisited regularly to consider new information and user/consumer feedback.
Image source: Pixabay.com


The desired output is greater insight into cyber threats, making room for faster, more targeted responses to them as well as proper development and allocation of IT and other resources.

Richard Blech is the CEO of Secure Channels, a company that offers customized data security solutions without compromising the level of protection provided while avoiding additional maintenance and support efforts. For similar reads, click here.


woensdag 28 maart 2018

Top cyber fraud trends in banking today

Financial institutions worldwide are facing a revolution in data access, artificial intelligence, and numerous disruptions that affect their legacy systems and processes. Then there are cyber fraud trends that hound their health in 2018. Here are some of the things they need to protect their customers, data, and organizations from. 

Image source: Pixabay.com

Unprecedented rise of mobile Banks will need to tighten their control on e-banking fraud, with mobile internet navigation more widely used today than computer navigation. The usual level of security typically found on mobile devices just doesn’t cut it anymore, needing new security layers such as those against SIM-switching. 

Scam explosion Certain scam attacks also exploit artificial intelligence (AI) technology, going on an industrial scale such as the use of robots to launch attacks. The scope is then much bigger and would entail real-time prevention and vigilance from the banks. 

Attacks via the underlying blockchain technologies of financial systems Nearly all of the large financial organizations worldwide are investing in systems based on blockchain technology, which comprises vulnerabilities and errors in implementation that can enable attackers to earn money and disrupt their regular work. 

ATM malware automation The first of these attacks occurred in 2009, and since then ATM machines have been on the radar of cyber fraudsters. Today this threat could reemerge as ATM malware-as-a-service, where a mini-computer connects automatically to an ATM, installs itself, and collects card data. 

Image source: Pixabay.com 

Richard Blech is the CEO of Secure Channels, a company that comes up with solutions designed to be customizable to its clients’ environment without compromising the level of protection it provides while avoiding additional maintenance and support efforts by support teams. Learn more on this page.

vrijdag 9 maart 2018

Of credit card transactions and online security

One can never overlook the importance of security when it comes to the internet. Cybercriminals are everywhere waiting for a chance to steal data, cash, and other valuables they can get their grimy hands on. An area that is under constant threat is that of credit card transactions. 

Image source: entrepreneur.com

Over the past few years, people and businesses have ignored the fact that online security is a significant part of transactions involving credit cards. In fact, Verizon Communications reported that 80 percent of global retailers are not up to code with their online security. This is a pressing concern since shoppers have expressed much anxiety toward the possibility of hackers breaching the retailers’ data and stealing information attached to their credit cards. 

Thankfully, technology is being developed to counter cyber theft of credit card info. Some companies have begun upgrading payment processes to allow only Europay Mastercard Visa microchips. The unique encryption generated during each transaction by these cards makes it more difficult for cybercriminals to get through, much less read, information. Although it may not be as convenient as previous credit cards, the security it provides is tighter and harder to crack. In the U.K. alone, using Europay Mastercard Visa has reduced domestic fraud by a third, which is a win by any standards. 

But this isn’t the only technique being used to protect online transactions. It’s fortunate for everyone that as hackers get more and more sophisticated, so does cybersecurity. 

Image source: TIME.com

Secure Channels CEO Richard Blech has data security, technology, and strategic alliances as his primary business focus. Read more about his industry on this blog.

dinsdag 27 februari 2018

Why organizations need to consider a key management solution

To secure every bit of information in an organization, various protection measures must be implemented. One of the most commonly chosen t00ls because of its capability to cover a lot of ground is data encryption. 

Image source: ophtek.com

Encryption is a form of cryptography, which is also called by some as the study of secret communication. It involves transforming plaintext or readable private information into something that appears nonsense so that third-party entities – named “adversaries,” in cryptography – cannot understand the data, should they get a hold of it. 

The intended recipients of the information are then provided with a means to decode it. In data encryption, the tool used to do is called a “key.” 

In an organization that employs data encryption, there can be countless keys involved, depending on the number of people, machines, and applications. To ensure efficiency and productivity, a key management system can be advantageous. 

Key management is the process of the generation, exchange, storage, use, and crypto-shredding of said keys. It can also be given the responsibility of distributing the keys to the pertinent users or groups. Moreover, some systems can monitor and record the instances when the keys are used for further protection. 

Image source: mil-embedded.com

Entrepreneur and innovator Richard Blech heads Secure Channels, which offers solutions that ensure the protection of client data from any form of theft. Mr. Blech is also a strong advocate of disruptive technology and strategic alliances. Read more about him by visiting this page.

donderdag 28 december 2017

Enemies at the gate: The rise of cyber-protection

History has seen its share of entities that have evolved to cope with the times. From fishes that developed legs to walk on land during prehistoric times to cavemen learning how to use fire and weapons to survive, evolution is a way to ensure things continue and improve. 

Image source: stlawu.edu

In today’s digital age, with the World Wide Web transforming into a world of its own, it was an inevitability that cyber-protection evolved to tackle the ever-growing threat of cybercriminals and dangerous programs that serve to destroy and promote anarchy. Without cyber-protection, as the world knows it today, cyberspace would be in complete disarray and total ruin. 

It was around 30 years ago when the first computer worm hit the web and hit it hard. A number of IT experts were quickly convinced that if a single program could be enough to bring the internet to its knees, something had to be done.

However, the safety programs back in the day were still not enough, as a new strain of malware had evolved into the Melissa and ILOVEYOU programs, affecting and damaging millions of PCs globally. 

Once again, a technological evolution had to happen to keep the world safe. IT experts came up with more aggressive antivirus programs and firewalls to combat the looming threat. Programs not only defended but also quarantined harmful files, and weren’t restricted to computers. They could now be used online as well. 

Today’s antivirus and anti-malware programs are much more sophisticated than ever before, which is for the best. Who knows what troubles cybercriminals may think of next? 

Image source: seasnet.ucla.edu

Secure Channels CEO Richard Blech is an entrepreneur, investor, and innovator. His primary business focus is on data security, technology, and strategic alliances. Visit this blog for more updates on the industry.

donderdag 30 november 2017

The malware that the FBI fears the most

While cybersecurity has evolved by leaps and bounds over the past decades, so have the methods of cybercriminals the world over. In fact, some of the dangerous programs existing in cyberspace today baffle even the best IT professionals. One such program is ransomware.

Image source: trendmicro.com
 
Ransomware is a type of malware that enters computer systems through email accounts. Like most harmful programs, ransomware presents itself as a harmless program that anyone can point and click on. A single click would cost a person around $500 dollars. Why? Because a single click can lock a computer and encrypt all the important files inside. The only way to open it up again is to pay the ransom, and receive the password.

Ransomware has earned the infamous reputation of being one of the very few programs the Federal Bureau of Investigation (FBI) has given up on. During one it’s fiercest attacks, ransomware left all IT experts in shambles, including those from the FBI. In fact, the FBI simply suggest that victims of this malware should just pay the ransom.

With a computer program of this caliber on the internet, IT and cybersecurity experts caution people when opening emails. The main point being that the strategy should be prevention until someone somewhere finds a way to reverse the effects of ransomware once it’s affected a computer and its files.

Image source: automationalley.com

 Secure Channels CEO Richard Blech is an entrepreneur, investor, and innovator. Learn more about his industry on this page.